Free PDF • 12 slides
AI governance, made auditable.
How SecuriX turns NIST AI RMF and ISO/IEC 42001 from policy documents into controls you can enforce and evidence.
337 KB • No sign-up needed
What's inside
From policy document to enforceable control.
The governance gap
Why policy stays on paper, AI usage stays invisible, and audit evidence stays manual.
Four pillars, one gateway
Data security and compliance, agentic data governance, budget and cost control, and operational governance.
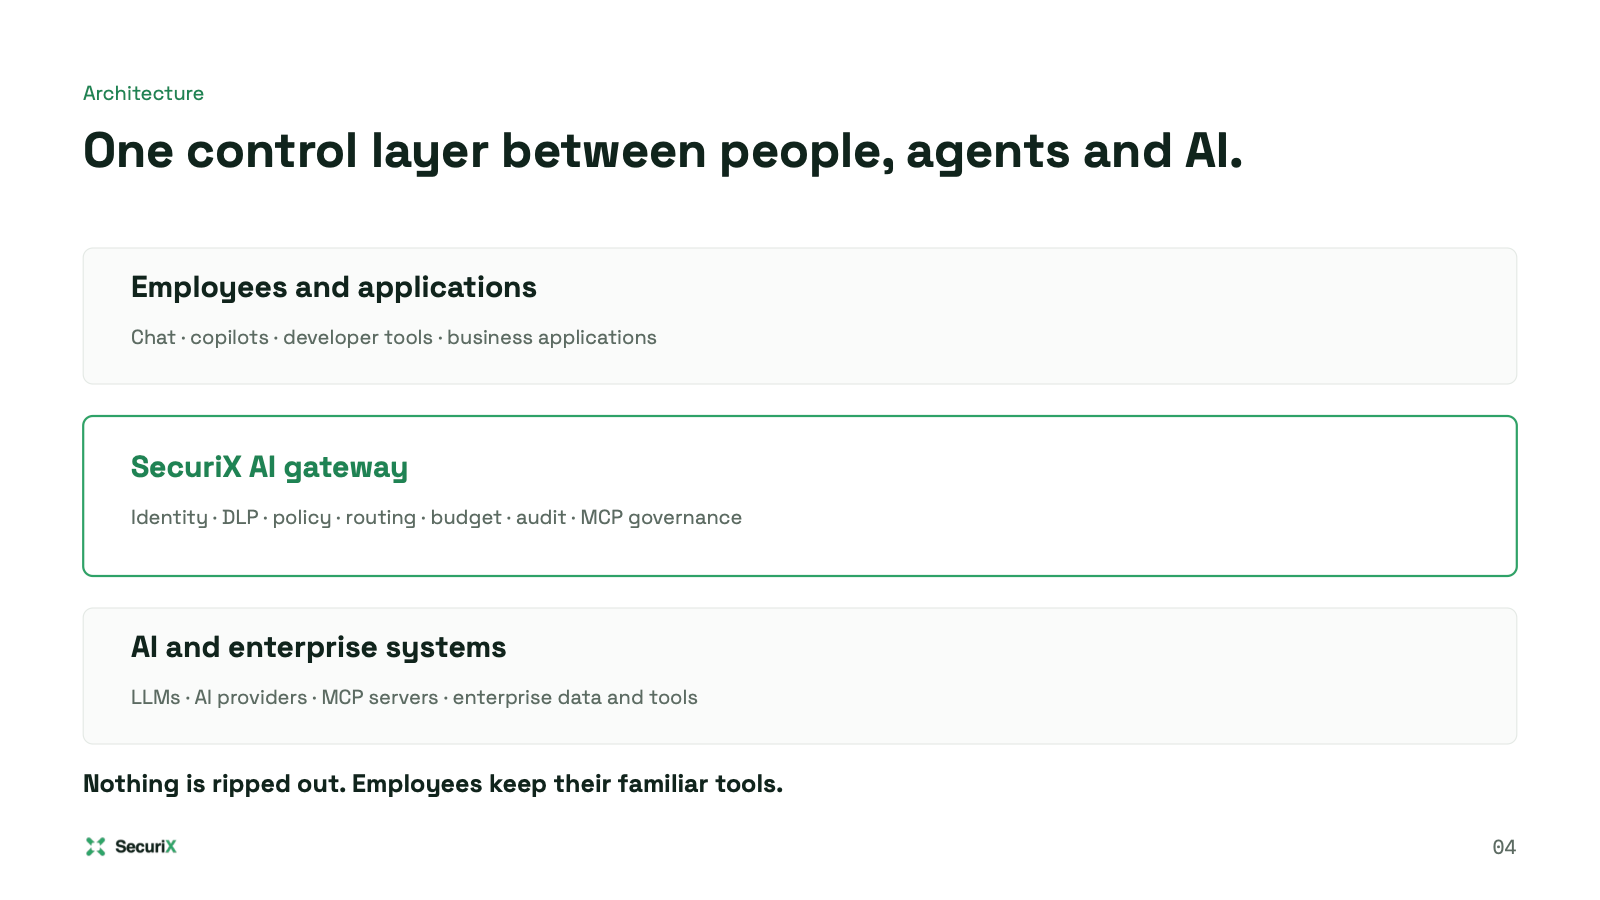
Architecture
One control layer between people, agents and AI, with nothing ripped out for employees.
NIST AI RMF
How runtime controls and evidence support Govern, Map, Measure and Manage.
ISO/IEC 42001
Evidence for Clauses 5, 6, 8 and 9-10, plus Annex A on data and third parties.
Operating model
A continuous loop: discover, assess, govern, enforce, monitor and prove.
Enterprise use cases
BFSI and NBFC, insurance, healthcare, BPO and shared services, manufacturing, and enterprise IT.
Next steps
A framework gap workshop, a scoped pilot on one AI workflow, and an evidence pack for your controls.
A look inside
Mapped to NIST AI RMF and ISO/IEC 42001.
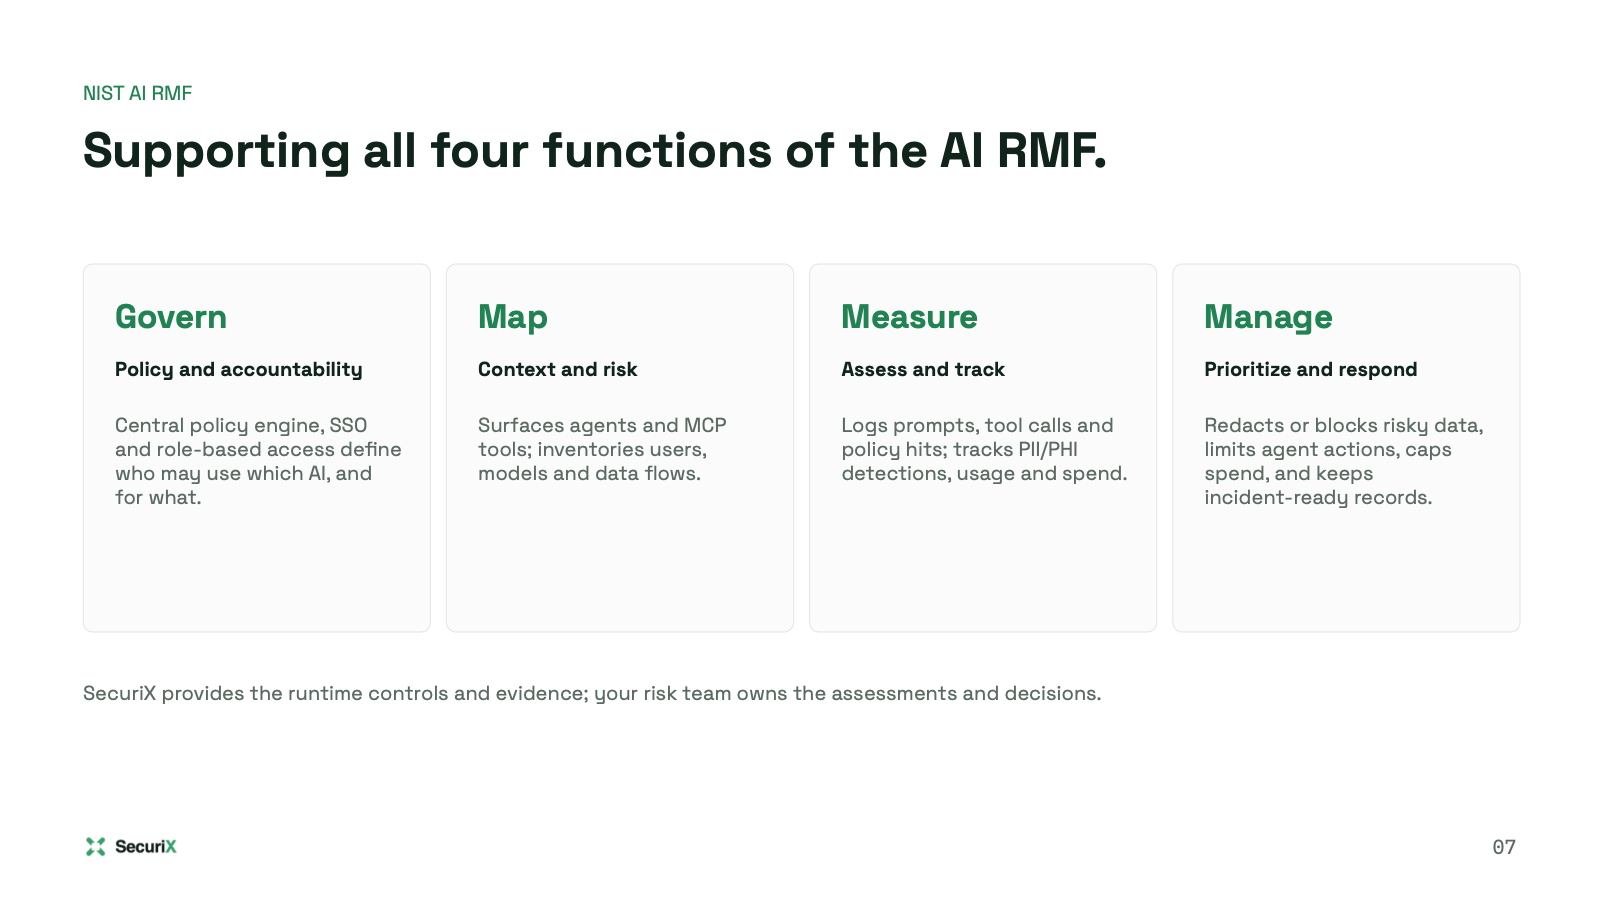
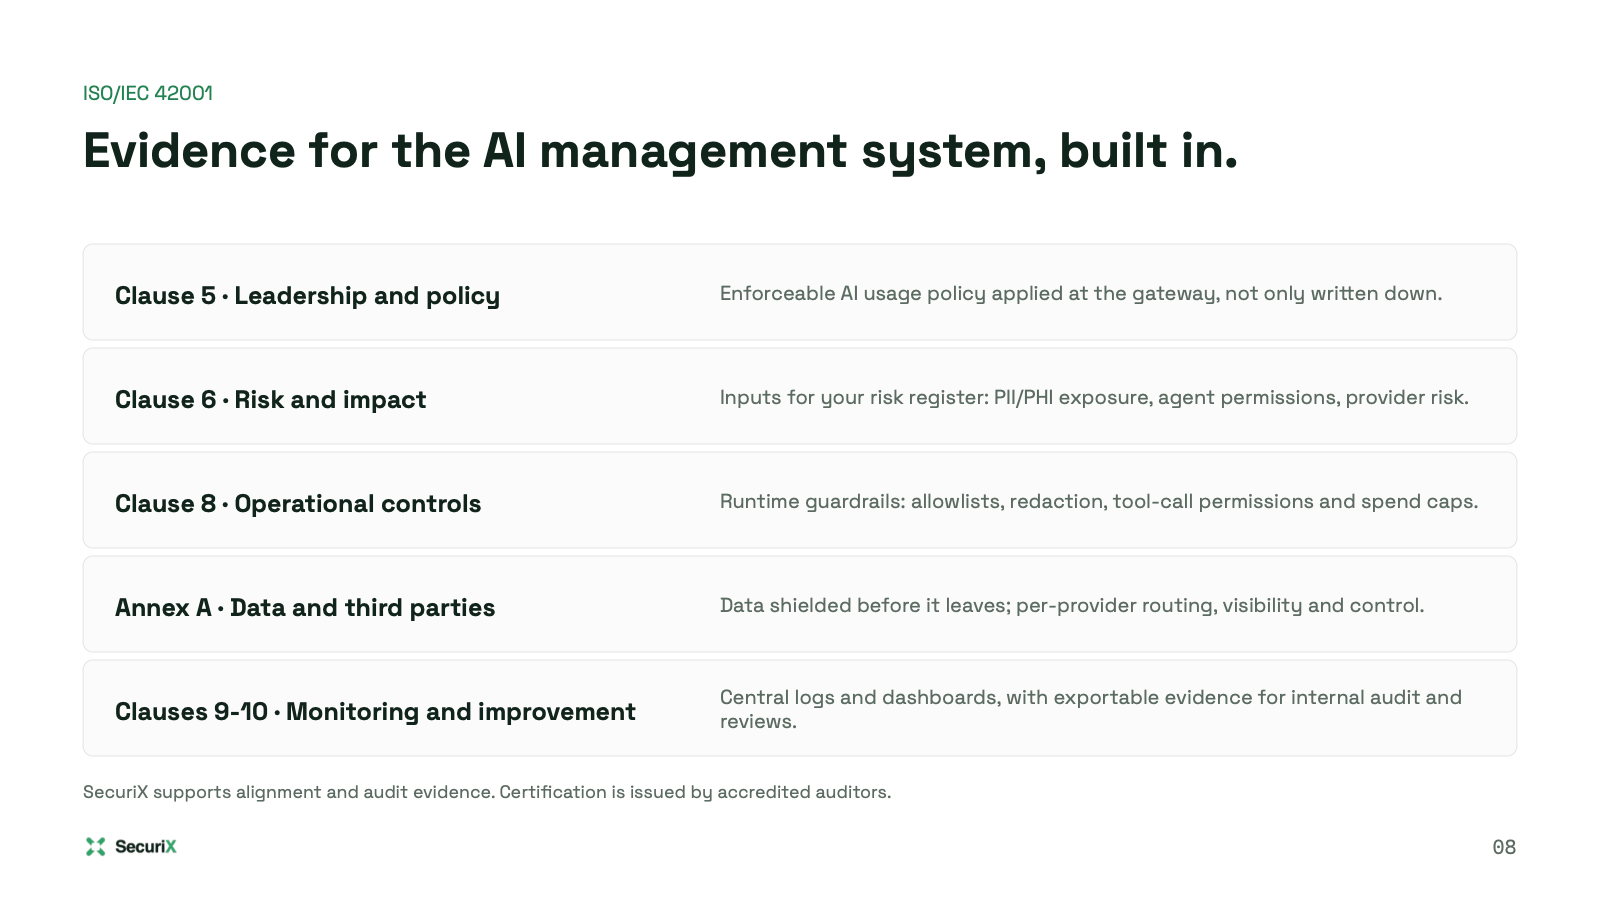
SecuriX provides the runtime controls and evidence; your risk team owns the assessments and decisions. SecuriX supports alignment and audit evidence. Certification is issued by accredited auditors.
Ready to govern AI responsibly?
Start with a framework gap workshop, a scoped pilot on one AI workflow, and an evidence pack for your controls.