- Published on
Beyond OAuth: Securing the Model Context Protocol (MCP)
The Model Context Protocol (MCP) has fundamentally changed how we connect AI agents to external tools and datasets. But as we rush to give autonomous agents access to enterprise and private data, we are relying on a security paradigm that was never designed for non-deterministic systems: OAuth.
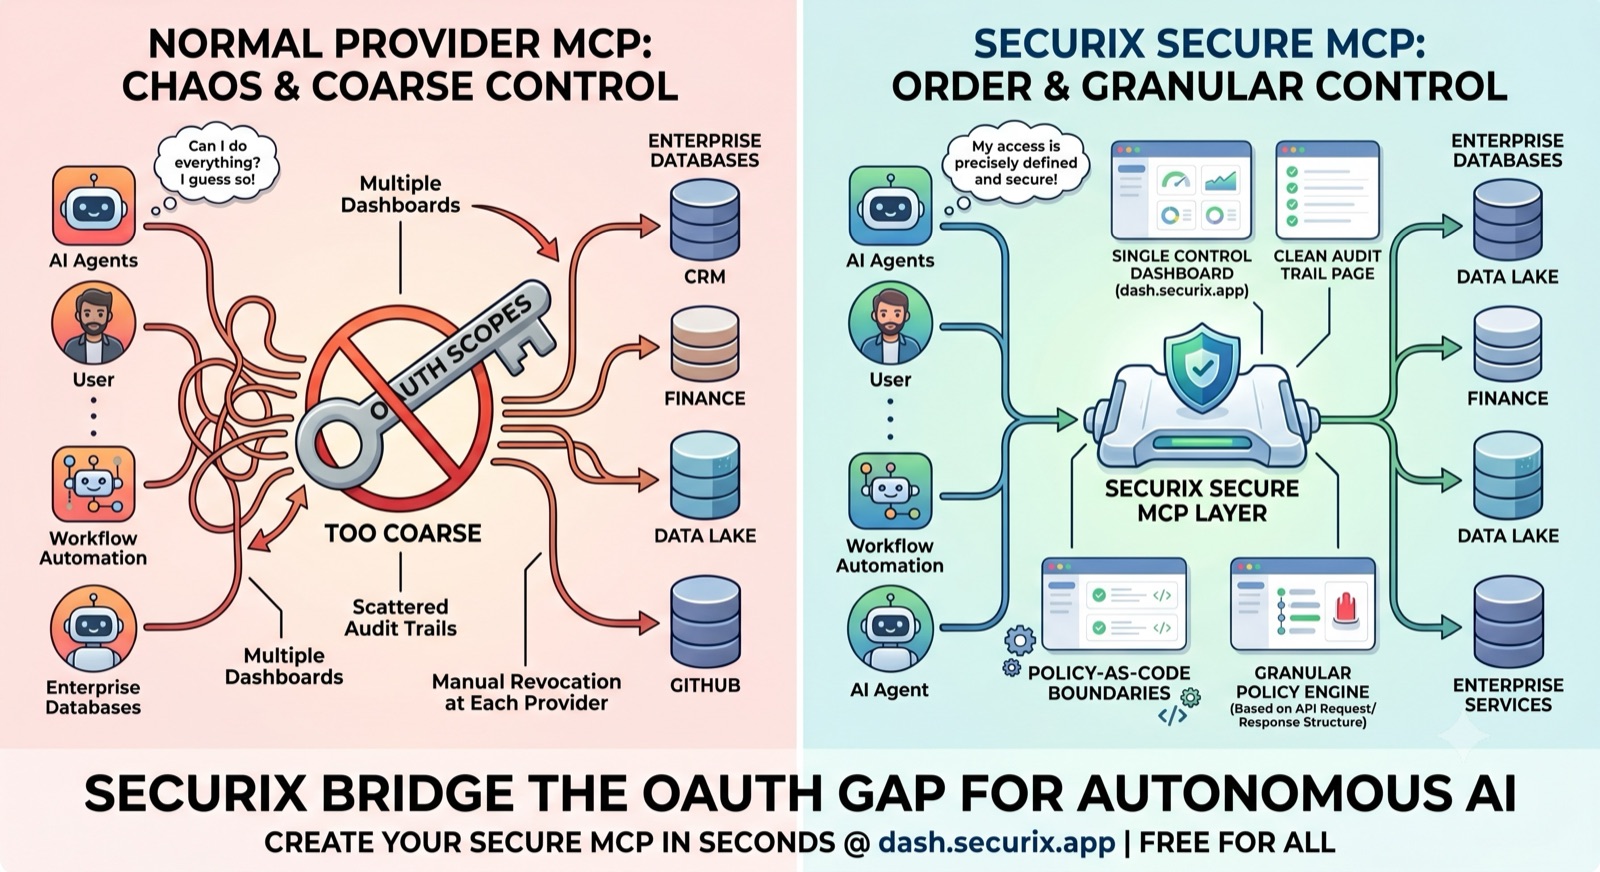
OAuth was built for human-to-data interactions or deterministic system-to-system connections. It is a coarse-grained mechanism. When you grant an AI agent "read/write" access via OAuth, you are handing over the keys to the kingdom. If the agent hallucinates, goes off-script, or is subjected to prompt injection, OAuth cannot stop it from taking destructive actions within those broad scopes.
To safely deploy autonomous AI in enterprise environments, we need an additional security infrastructure layer. Here is how a standard Provider MCP Connection compares to using SecuriX’s Secure MCP Connection to bridge this gap.
The Architectural Difference
| Feature | Standard Provider MCP | SecuriX Secure MCP |
|---|---|---|
| Integration | Separate MCP setup for each provider | Single MCP URL for multiple providers |
| Access Control | Coarse OAuth scopes | Granular API request/response policies |
| Revocation | Manual removal at each 3rd-party site | Centralized kill switches in one dashboard |
| Visibility | Scattered, inconsistent provider logs | Unified audit trail across all agents |
| Cost | Free (Often default in directories) | Free (Custom connector / directory pending) |
The 6 Core Benefits of the SecuriX Secure MCP
1️⃣ One Unified Hub for Agents and Providers Instead of juggling individual MCPs for every tool, SecuriX allows you to select the providers you want and generate a single MCP URL in seconds. You can easily map providers to agents. Need a new agent with a completely different set of tools? Just select the providers, create a new agent profile, and generate a fresh MCP URL instantly at dash.securix.app.
2️⃣ Granular, Deterministic Policies (Beyond OAuth) You can no longer depend solely on OAuth scopes to set boundaries for chatbots. SecuriX provides a clean policy engine to define exactly what your AI can and cannot do based on the precise structure of the API request and response objects. This deterministic Policy-as-Code approach is impossible with a standard provider MCP.
3️⃣ A Single Place of Control If you need to revoke an agent's access, standard MCPs force you to log into every individual 3rd-party provider to sever the connection. SecuriX acts as your centralized control plane. You can instantly sever any provider connection directly from your dashboard.
4️⃣ A Clean, Unified Audit Trail Currently, checking what your agent actually did requires relying on whatever reporting (if any) the individual providers offer, forcing you to piece together logs across multiple platforms. SecuriX intercepts the traffic and provides a comprehensive, single-page audit trail of all API calls made by your agents.
5️⃣ Frictionless Routing Both approaches are completely free to use. While standard provider MCPs might be available by default in connector directories, setting up SecuriX is as simple as adding a custom connector in Claude or enabling dev mode in ChatGPT (and we are actively working on submitting SecuriX to these directories for native discovery).
6️⃣ Built for the Autonomous Future By placing SecuriX between your agents and your data, you transform a fragile, distributed web of coarse permissions into a secure, observable, and tightly controlled AI infrastructure.
Ready to secure your AI interacting with your data? Set up your first secure MCP URL in seconds at https://dash.securix.app.
See SecuriX in front of your own traffic.
Tell us where to reach you and we'll set up a walkthrough with your identity provider, your policies, and your budget structure.